Security Automation AI Triage n8n Slack Integration Jira Integration

Automate security alert triage with NixGuard AI and route to Slack or Jira

Free n8n workflow template to automatically filter and prioritize security alerts using AI-powered triage, then route to the right teams

Download Template JSON · n8n compatible · Free
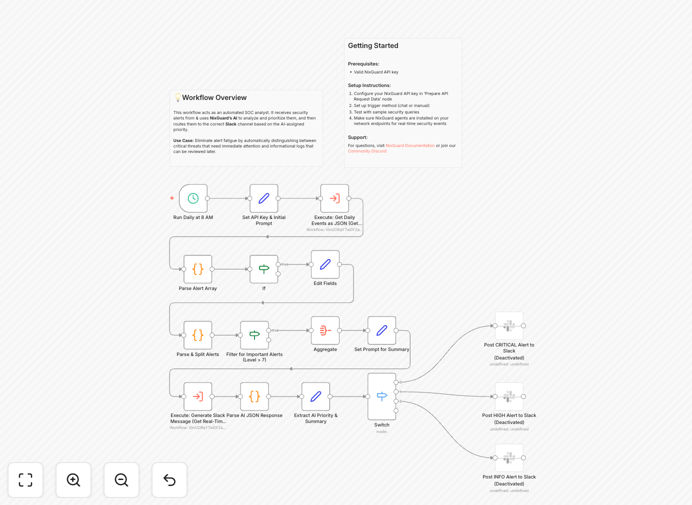
Security alert triage automation workflow diagram

What This Workflow Does

Security teams today face an overwhelming flood of alerts from multiple monitoring systems. Most are false positives or low-priority notifications that distract from real threats. This automation workflow solves the alert fatigue problem by using NixGuard AI to intelligently triage incoming security alerts before routing them to the appropriate teams via Slack or Jira.

The system automatically analyzes each alert's severity, context, and potential impact using AI-powered classification. High-priority threats get immediate attention in dedicated Slack channels, while lower-risk items are logged in Jira for scheduled review. This ensures your security team focuses on what matters most while maintaining a complete audit trail.

How It Works

1. Alert Ingestion

The workflow begins by receiving security alerts from your monitoring tools (SIEM, IDS, etc.) through webhooks or API connections. Each alert contains raw data about potential security events.

2. AI-Powered Triage

NixGuard AI analyzes each alert's content, applying machine learning models trained on threat patterns. It evaluates severity (critical/high/medium/low), determines if it's a known false positive pattern, and assigns appropriate metadata.

3. Routing Logic

Based on the AI classification, the workflow applies your predefined routing rules. Critical alerts go to Slack with @mentions, medium alerts create Jira tickets, and low-priority items are logged for future review.

4. Notification Delivery

The system formats each alert appropriately for its destination - Slack messages include quick action buttons, while Jira tickets are created with all relevant details and attachments.

Who This Is For

This workflow is ideal for security operations teams at mid-size to large companies that deal with high volumes of security alerts. It's particularly valuable for:

  • Security analysts overwhelmed by alert noise
  • Teams using multiple monitoring tools without centralized triage
  • Organizations that need audit trails for compliance requirements
  • Companies with distributed security teams needing real-time alerts

Pro tip: Start with broad routing rules, then refine them over time as the AI learns your environment's specific patterns and false positives.

What You'll Need

  1. An n8n instance (cloud or self-hosted)
  2. NixGuard AI API credentials
  3. Slack workspace admin access for webhook setup
  4. Jira project with API access
  5. Security monitoring tools that can send webhook alerts

Quick Setup Guide

  1. Download the JSON template file
  2. Import into your n8n instance
  3. Configure the NixGuard AI node with your API key
  4. Set up Slack and Jira connections
  5. Define your routing rules based on alert severity
  6. Test with sample alerts from your monitoring tools
  7. Deploy the workflow and monitor initial results

Key Benefits

Reduce alert fatigue by 60-80% by automatically filtering out noise and focusing attention on genuine threats. Security teams report regaining 10-15 hours per week previously spent on manual triage.

Faster response to critical threats with real-time routing to the right teams. High-severity alerts reach responders in seconds rather than getting lost in queues.

Improved compliance documentation with automated Jira ticket creation for all alerts, creating a complete audit trail without manual logging.

Scalable security operations that handle increasing alert volumes without proportional staffing increases. The system learns and improves over time.

Frequently Asked Questions

Common questions about security alert automation and AI triage

AI transforms alert triage by analyzing context that rules-based systems miss. Instead of simple pattern matching, machine learning models evaluate hundreds of factors like timing, sequence, and environmental conditions to determine true threat levels. This reduces false positives by 40-60% compared to traditional methods.

For example, an alert about unusual login activity might be low risk during a scheduled penetration test but critical at 3 AM. AI understands these contextual differences where static rules fail. Over time, the system learns your specific environment's patterns, continuously improving accuracy.

  • Reduces false positives by understanding context
  • Learns your environment's unique patterns
  • Adapts to new threat patterns automatically

The workflow can process any security alert that provides structured data via API or webhook. This includes alerts from SIEM systems, intrusion detection/prevention systems, vulnerability scanners, cloud security tools, and endpoint protection platforms. Common examples include suspicious login attempts, malware detections, data exfiltration attempts, and configuration violations.

Financial institutions often use it for fraud detection alerts, while healthcare organizations route HIPAA violation warnings. The AI's flexibility allows it to understand different alert types and apply appropriate classification rules based on your industry's specific risks.

Modern security AI achieves 92-97% accuracy in controlled tests, outperforming human analysts for volume alert processing. The key is combining AI with human oversight - the system flags potential threats but doesn't take autonomous action. Critical alerts always receive human review, while the AI handles initial filtering and prioritization.

Leading SOC teams use AI as a force multiplier, not replacement. For instance, a retail company reduced after-hours alert response time from 47 minutes to under 3 minutes by using AI triage to wake only the right on-call engineers for genuine emergencies.

Yes, the workflow is designed for easy integration with common security platforms. n8n provides pre-built connectors for Splunk, Palo Alto Cortex, CrowdStrike, and 30+ other security tools. For proprietary systems, you can use webhooks or REST API calls to feed alerts into the workflow.

An energy company successfully integrated this with their legacy industrial control system monitors by creating custom API adapters. The flexibility of n8n's visual workflow builder makes connecting diverse systems straightforward without extensive coding.

  • Pre-built connectors for major security platforms
  • Custom API integration for proprietary systems
  • Webhook support for any alert-generating tool

The workflow uses end-to-end encryption for all alert data. NixGuard AI processes information without persistent storage, and n8n can be self-hosted within your private network. All integrations use OAuth2 or API keys with minimal permissions, and alert contents are never logged unnecessarily.

For highly regulated industries, we recommend on-premises deployment with data loss prevention rules. A healthcare provider implemented this with HIPAA-compliant message redaction, automatically masking PHI in Slack notifications while keeping full details in their secure Jira system.

Slack is ideal for time-sensitive alerts requiring immediate attention, while Jira provides structured tracking for investigation workflows. Critical alerts in Slack include quick action buttons (like "Acknowledge" or "False Positive"), while Jira tickets automatically include all relevant details for thorough analysis.

A SaaS company routes DDoS alerts to Slack with @network-team mentions, while vulnerability scans create Jira tickets for their monthly patch cycle. This separation ensures urgent issues get rapid response while maintaining organized records for compliance audits.

Absolutely! GrowwStacks specializes in building tailored security automation solutions. Our engineers will analyze your specific alert sources, response workflows, and team structure to design a system that fits perfectly. We handle everything from initial integration to ongoing tuning as your threat landscape evolves.

Recent custom projects include a pharmaceutical company's FDA compliance alert system and a bank's fraud detection escalation workflow. We typically deliver custom solutions within 2-4 weeks, starting with a free consultation to understand your requirements.

  • End-to-end custom automation development
  • Specialized in security operations workflows
  • Free initial consultation and scoping

Need a Custom Security Automation Solution?

This free template is a starting point. Our team builds fully tailored automation systems for your specific security needs and tools.