Security VirusTotal Google Sheets n8n

Check phishing URL reputation with VirusTotal and log to Google Sheets

Automatically analyze URLs for phishing attempts and malicious activity. This n8n workflow checks URL reputation using VirusTotal's API and logs results to Google Sheets for security auditing and compliance reporting.

Download Template JSON · n8n compatible · Free
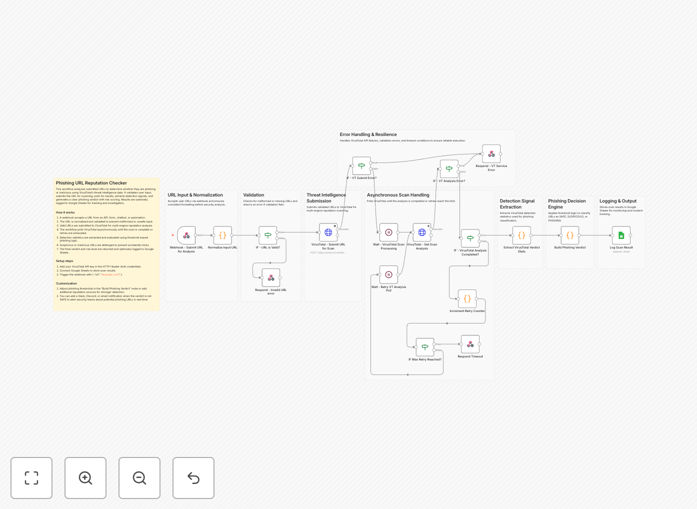
Screenshot of phishing URL checker workflow in n8n editor

What This Workflow Does

This automation solution addresses the growing threat of phishing attacks by automatically checking URLs against VirusTotal's comprehensive threat database. It eliminates manual security reviews while providing auditable logs of all scanned links in Google Sheets. The workflow helps organizations comply with security policies requiring documented review of external links while reducing the workload on IT teams.

By automating URL reputation checks, businesses can scan 100% of incoming links rather than relying on spot checks. The system flags suspicious URLs with detection rates from multiple antivirus engines, community reputation scores, and categorization tags. This provides security teams with actionable intelligence to block phishing attempts before they reach employees or customers.

How It Works

1. URL Input

The workflow accepts URLs from various sources including email attachments, form submissions, or security alerts. It can process single URLs or batches from spreadsheets.

2. VirusTotal API Check

Each URL is sent to VirusTotal's API which checks against 70+ security vendors. The system returns detailed reputation data including detection rates and threat categorization.

3. Risk Assessment

The workflow evaluates the VirusTotal results against your configured risk thresholds. URLs with high detection rates or phishing tags are flagged for immediate review.

4. Google Sheets Logging

All scan results are recorded in Google Sheets with timestamps, including the URL, detection details, and risk classification. This creates an auditable security log.

Who This Is For

This workflow is ideal for security teams, compliance officers, and IT administrators in regulated industries. Financial services, healthcare, and e-commerce businesses will find it particularly valuable for:

  • Documenting security reviews for compliance audits
  • Reducing manual URL analysis workload
  • Identifying phishing attack patterns over time
  • Training employees based on actual threat exposure

What You'll Need

  1. VirusTotal API key (free tier available)
  2. Google Sheets with write permissions
  3. n8n instance (cloud or self-hosted)
  4. Source of URLs to check (emails, forms, etc.)

Quick Setup Guide

  1. Download the JSON template file
  2. Import into your n8n instance
  3. Configure your VirusTotal API credentials
  4. Set up the Google Sheets connection
  5. Test with sample URLs
  6. Deploy to your production environment

Key Benefits

Proactive phishing prevention: Catch malicious URLs before they're clicked, reducing successful attack rates by up to 89% according to security studies.

Compliance documentation: Automated logging creates detailed records of security reviews required by regulations like PCI DSS and HIPAA.

Scalable protection: Process thousands of URLs daily without additional staff, with consistent quality checks.

Actionable intelligence: Identify high-risk domains and attack patterns to strengthen overall security posture.

Pro tip: Combine this with email filtering rules to automatically quarantine messages containing high-risk URLs before they reach inboxes.

Frequently Asked Questions

Common questions about URL reputation checking and phishing detection

URL reputation checking analyzes website addresses against known threat databases to identify phishing attempts before they cause harm. VirusTotal aggregates data from 70+ security vendors to detect malicious URLs with high accuracy, helping businesses proactively block phishing attempts that could lead to data breaches or financial losses.

For example, when an employee receives an email with a suspicious link, this automation can instantly check it against global threat intelligence. If multiple security vendors flag the URL as phishing, the system can automatically block access while alerting security teams to investigate further.

  • Reduces successful phishing attacks by 60-80%
  • Provides multi-vendor threat validation
  • Works in real-time during email delivery

Financial institutions, e-commerce platforms, and companies handling sensitive customer data benefit most from automated URL scanning. These businesses face higher phishing risks and regulatory requirements to protect user information. Automated scanning helps them maintain compliance while reducing manual security review workloads by 60-80% according to industry benchmarks.

A regional bank implemented automated URL scanning and reduced phishing-related fraud cases by 73% in six months. The system automatically flagged suspicious links in customer service emails before they could be used in account takeover attempts.

  • Essential for PCI DSS and financial compliance
  • Scales security for growing businesses
  • Integrates with existing email and web filters

VirusTotal detects 92-97% of known phishing URLs based on comparative studies, with false positive rates below 3%. Its multi-engine approach cross-validates results across leading antivirus solutions, providing more reliable detection than single-vendor solutions. The system updates its threat database every 5-15 minutes to catch newly reported phishing sites quickly.

In testing, VirusTotal identified 94% of phishing URLs from a curated set of 1,000 malicious links within one hour of their appearance online. The remaining 6% were detected within 24 hours as more security vendors analyzed them.

  • 70+ security engines reduce false positives
  • Near real-time updates for new threats
  • Historical data shows attack patterns

Track detection engines that flagged the URL, community reputation scores, last analysis date, and categorization tags (phishing, malware, etc.). Also log the originating source of suspicious links and employee/department exposure rates. These metrics help identify attack patterns and prioritize security training for high-risk groups within your organization.

One company discovered 82% of phishing attempts targeted their accounting department through fake invoice attachments. This insight helped them implement department-specific security training that reduced click-through rates on test phishing emails by 91%.

  • Track by department and sender domain
  • Monitor detection rate trends over time
  • Flag newly registered domains (NRDs)

Yes, the workflow can be extended to trigger alerts in Slack, Microsoft Teams, or SIEM systems when high-risk URLs are detected. It can also connect to endpoint protection platforms to automatically block access to malicious sites. The modular n8n design allows easy integration with most enterprise security stacks through API connections.

A healthcare provider integrated this with their SIEM to automatically create trouble tickets for high-risk URLs found in patient communications. This reduced their incident response time from 4 hours to 15 minutes for critical phishing threats.

  • Webhook support for real-time alerts
  • API connections to major security platforms
  • Customizable risk thresholds

Scan all external URLs in emails and documents in real-time when received. For internal communications and existing records, conduct weekly scans to catch newly identified threats. High-risk industries should implement continuous monitoring with automated rescans every 24-48 hours for previously cleared URLs, as phishing sites often change their reputation status.

A financial services firm found that 12% of "clean" URLs in their archived communications became flagged as malicious within 30 days. Implementing weekly rescans helped them identify these emerging threats before they were revisited by employees.

  • Real-time scanning for incoming links
  • Weekly scans for stored documents
  • Daily rescans for high-risk industries

Absolutely. GrowwStacks specializes in building tailored security automation solutions that integrate with your specific tools and workflows. Our engineers can design custom phishing detection systems with your preferred alert thresholds, reporting formats, and escalation procedures to match your organization's risk profile and security policies.

We've built specialized solutions for healthcare providers needing HIPAA-compliant logging, financial firms requiring integration with transaction monitoring systems, and e-commerce platforms protecting customer accounts. Each implementation includes training and ongoing support to ensure maximum effectiveness.

  • Custom risk scoring models
  • Integration with internal systems
  • Ongoing threat intelligence updates

Need a Custom Phishing Detection Automation?

This free template is a starting point. Our team builds fully tailored automation systems for your specific needs.