Security Data Protection n8n Automation

Monitor data breaches in real-time with Have I Been Pwned

Automated monitoring for new data breaches with instant alerts when your data appears in breaches

Download Template JSON · n8n compatible · Free
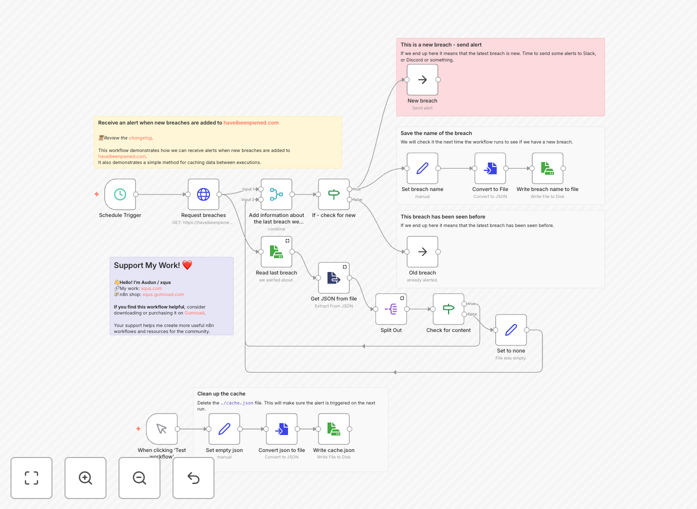
Have I Been Pwned monitoring workflow dashboard

What This Workflow Does

This n8n workflow automates the monitoring of data breaches using the Have I Been Pwned service. It continuously checks whether your email addresses, domains, or passwords appear in new data breaches and sends immediate alerts when compromised credentials are detected.

The solution solves the critical problem of delayed breach discovery, which often leaves sensitive accounts vulnerable for weeks or months. By automating the monitoring process, you reduce response times from days to minutes, significantly improving your security posture against credential stuffing attacks and account takeovers.

How It Works

1. Scheduled breach checks

The workflow runs on a schedule you define (hourly, daily, etc.) to check Have I Been Pwned's breach database. It can monitor multiple email addresses or domains simultaneously through API calls to the service.

2. Breach detection

When the workflow finds a match in breach data, it extracts detailed information including the breach name, date, and types of data exposed (emails, passwords, credit cards, etc.). This context helps prioritize response actions.

3. Alert notifications

Upon detecting compromised credentials, the workflow triggers customizable alerts through your preferred channels (email, Slack, SMS, etc.). Notifications include all relevant breach details and recommended actions.

Who This Is For

This workflow is essential for security teams, IT administrators, and developers responsible for protecting user accounts and company data. It's equally valuable for individuals who want to monitor their personal email addresses and passwords.

Businesses with multiple employees or customer accounts benefit most, as manual monitoring becomes impractical at scale. The automated solution ensures consistent protection across all accounts without requiring individual users to check breach statuses themselves.

What You'll Need

  1. An n8n instance (cloud or self-hosted)
  2. Have I Been Pwned API access (free tier available)
  3. Notification channel credentials (email server, Slack webhook, etc.)
  4. List of email addresses or domains to monitor

Quick Setup Guide

  1. Download the workflow template file
  2. Import it into your n8n instance
  3. Configure your email addresses/domains to monitor
  4. Set up your preferred notification channels
  5. Adjust the schedule frequency as needed
  6. Test with known compromised credentials to verify alerts

Key Benefits

Reduce breach response time from days to minutes by eliminating manual checking and receiving instant alerts when your data appears in new breaches.

Protect against credential stuffing attacks by identifying compromised passwords before attackers can use them to access your accounts.

Maintain compliance with security best practices by demonstrating proactive monitoring of credential exposure across your organization.

Scale protection across all users without requiring individual employees or customers to monitor their own accounts.

Integrate with existing security tools to automatically trigger password resets, account lockdowns, or other protective measures.

Frequently Asked Questions

Common questions about data breach monitoring and automation

Have I Been Pwned is a free service that aggregates data from breaches and allows users to check if their email or password has been compromised. It provides detailed information about which breaches contained your data and what information was exposed.

Businesses use it to monitor employee credentials and alert users when their accounts appear in new breaches. The service maintains one of the most comprehensive breach databases available, with over 11 billion compromised accounts from hundreds of breaches.

  • Tracks both email addresses and passwords
  • Includes detailed breach metadata
  • Free API access available

Automating breach monitoring provides immediate alerts when credentials appear in new breaches, allowing faster response times. Manual checking is time-consuming and often delayed, while automation runs continuous checks in the background.

This reduces the window of vulnerability between a breach occurring and users taking protective actions like password changes. Automated systems can also enforce consistent monitoring across all accounts, eliminating human oversight.

  • 24/7 monitoring without manual effort
  • Consistent protection across all accounts
  • Integration with other security systems

This workflow can monitor email addresses, domains, and passwords against Have I Been Pwned's database. It checks for compromised credentials in both public data breaches and pastes (data shared on sites like Pastebin).

The service covers over 11 billion compromised accounts from hundreds of breaches, making it one of the most comprehensive sources available. You can monitor individual accounts or entire domains for exposure.

  • Email addresses and domains
  • Passwords (hashed for security)
  • Breach metadata and details

For critical systems, continuous monitoring is ideal as new breaches occur daily. This workflow can be scheduled to run hourly or daily checks depending on security needs.

High-risk industries like finance should monitor more frequently than less sensitive operations. The key is balancing security needs with API rate limits and system resources to maintain effective protection.

  • Critical systems: hourly checks
  • Standard business: daily checks
  • Adjust based on risk profile

Immediately force password resets for affected accounts and enable multi-factor authentication. Review account activity for suspicious behavior and consider security awareness training.

For businesses, notify affected employees or customers with clear instructions. Document the incident response process for compliance purposes and analyze how the credentials were compromised to prevent future incidents.

  • Force password changes
  • Enable MFA where possible
  • Review account activity logs

Yes, the workflow can be extended to integrate with password managers, identity providers, or SIEM systems. Common integrations include automatically revoking compromised API keys, disabling user accounts, or creating tickets in IT service management tools.

The modular design allows adding notification channels like Slack, Microsoft Teams, or SMS alerts. You can also connect it to your identity management system to automatically flag compromised accounts.

  • Password managers (1Password, LastPass)
  • Identity providers (Okta, Azure AD)
  • SIEM and logging systems

Absolutely. GrowwStacks specializes in building tailored security automation solutions. We can create custom workflows that integrate Have I Been Pwned with your existing security stack, add enterprise features like role-based alerts, and ensure compliance with your security policies.

Our team will design a solution that fits your specific risk profile and operational needs, whether you need to monitor thousands of employee accounts or protect customer data at scale. We handle everything from initial consultation to implementation and ongoing support.

  • Custom integrations with your tools
  • Enterprise-grade security features
  • Ongoing maintenance and support

Need a Custom Data Breach Monitoring Solution?

This free template is a starting point. Our team builds fully tailored automation systems for your specific security needs.